Bitpanda and Fibank: crypto inside a banking app
Bulgaria's Fibank will offer crypto through Bitpanda in its My Fibank app. What the partnership means, and what stays the same for you.
Researchers found 17 fake Skrill, Neteller and Paysafe packages on npm and PyPI that steal API keys and tokens. Wallet users are not the target.
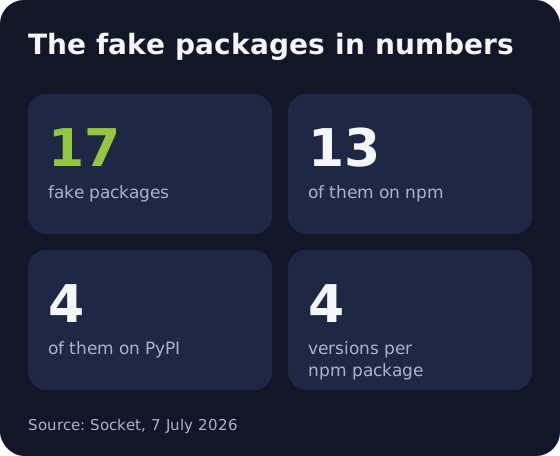
Security firm Socket has found 17 fake software packages that imitate the Skrill, Neteller and Paysafe developer kits on npm and PyPI. They steal API keys and access tokens from the machines of developers who install them. If you only use a Skrill or Neteller wallet, you are not the target.
Socket published its report on 7 July 2026. According to the report, 13 packages on npm and 4 on PyPI appeared almost at the same time. Names such as skrill, skrill-sdk, neteller and paysafe-checkout are meant to look like official tools. Each npm package came in four versions (1.0.0 to 1.0.3), and Socket’s scanner flagged all of them within 6 minutes of publication. Source: Socket, also covered by BleepingComputer on 8 July.
They offer the same functions as a real payment kit but never contact Paysafe. They return made-up success messages instead, so a test run looks fine. In the background they read environment variables whose names contain KEY, SECRET, TOKEN, PASS, AUTH or API. Socket names PAYSAFE_API_KEY, AWS_SECRET_ACCESS_KEY, GITHUB_TOKEN and NPM_TOKEN as examples. The npm packages send data only when a Paysafe API key is set. The PyPI packages start on import and need no key.
Nothing in the reports says customer accounts were hit. The damage falls on developers and build servers: a stolen key can open access to payment tests, cloud accounts or code repositories. A normal Skrill or Neteller wallet needs no such package.
The sources do not say whether Paysafe has commented, and they do not name who is behind the campaign. Socket describes the attacker as technically skilled and expects them to try again. For wallet users, the usual advice still applies: spot fake Skrill pages and switch on two-factor login.
Bulgaria's Fibank will offer crypto through Bitpanda in its My Fibank app. What the partnership means, and what stays the same for you.
Paysafe is now title partner of a Formula E team. For Skrill and Neteller accounts, fees, limits and products stay as they are.
Bitpanda and Raiffeisen Bank International agree a group-wide framework for crypto services in 11 CEE markets. What it means for buying crypto.